
Nooga Risk
Nooga Scale
Compliance
Risk Management
Governance, Risk and Compliance that keeps up with delivery
Regulated organisations shouldn't have to choose between shipping fast and staying compliant. Nooga embeds governance directly into workflows in Azure DevOps, enabling risk management and compliance at the pace of delivery.
What Nooga Solves
Why do Governance, Risk and Compliance (GRC) still run on a separate track from delivery?

Compliance lives in documents. Risk management in spreadsheets. Delivery in collaboration platforms.
Your governance and compliance policies sit in SharePoint folders and shared drives. Risk management ends up documented in Excel spreadsheets or separate GRC tools. Delivery sits in Azure DevOps.

Every release waits for a manual check.
Product teams stop to gather evidence, fill out checklists, and chase approvals before they can ship. But those risks should have informed the build and design decisions made weeks earlier — the risk register is only reviewed quarterly, or twice a year, long after those decisions were already made.

Risk and Compliance become the bottlenecks
Risk and Compliance teams can't scale 1:1 with delivery, and the regulatory and security landscape keeps growing regardless. Treated as separate processes, both become bottlenecks delivery has to wait for.

Audits run on stale evidence.
When audit time comes, teams scramble to build the audit trail after the fact, reconstructing what happened from scattered sources. The risks that mattered were never surfaced in time to shape what to prioritise, how to build securely, or whether you were on track to meet your commitments.
How Nooga Solves It
Governance, Risk and Compliance built-in, not bolted on
Governance by design builds risk management and compliance into the workflows where work actually happens, moving at the same pace as delivery instead of running out of sync.
1. Manage risks where your teams plan and deliver
Nooga adds risk directly to the work items your teams already use in Azure DevOps — features, epics, objectives. The ROAM view in Nooga Scale lets you raise and assess risks at the same cadence as planning and delivery, not on a separate quarterly cycle. Score each risk on likelihood and impact, and focus on the ones that actually matter.
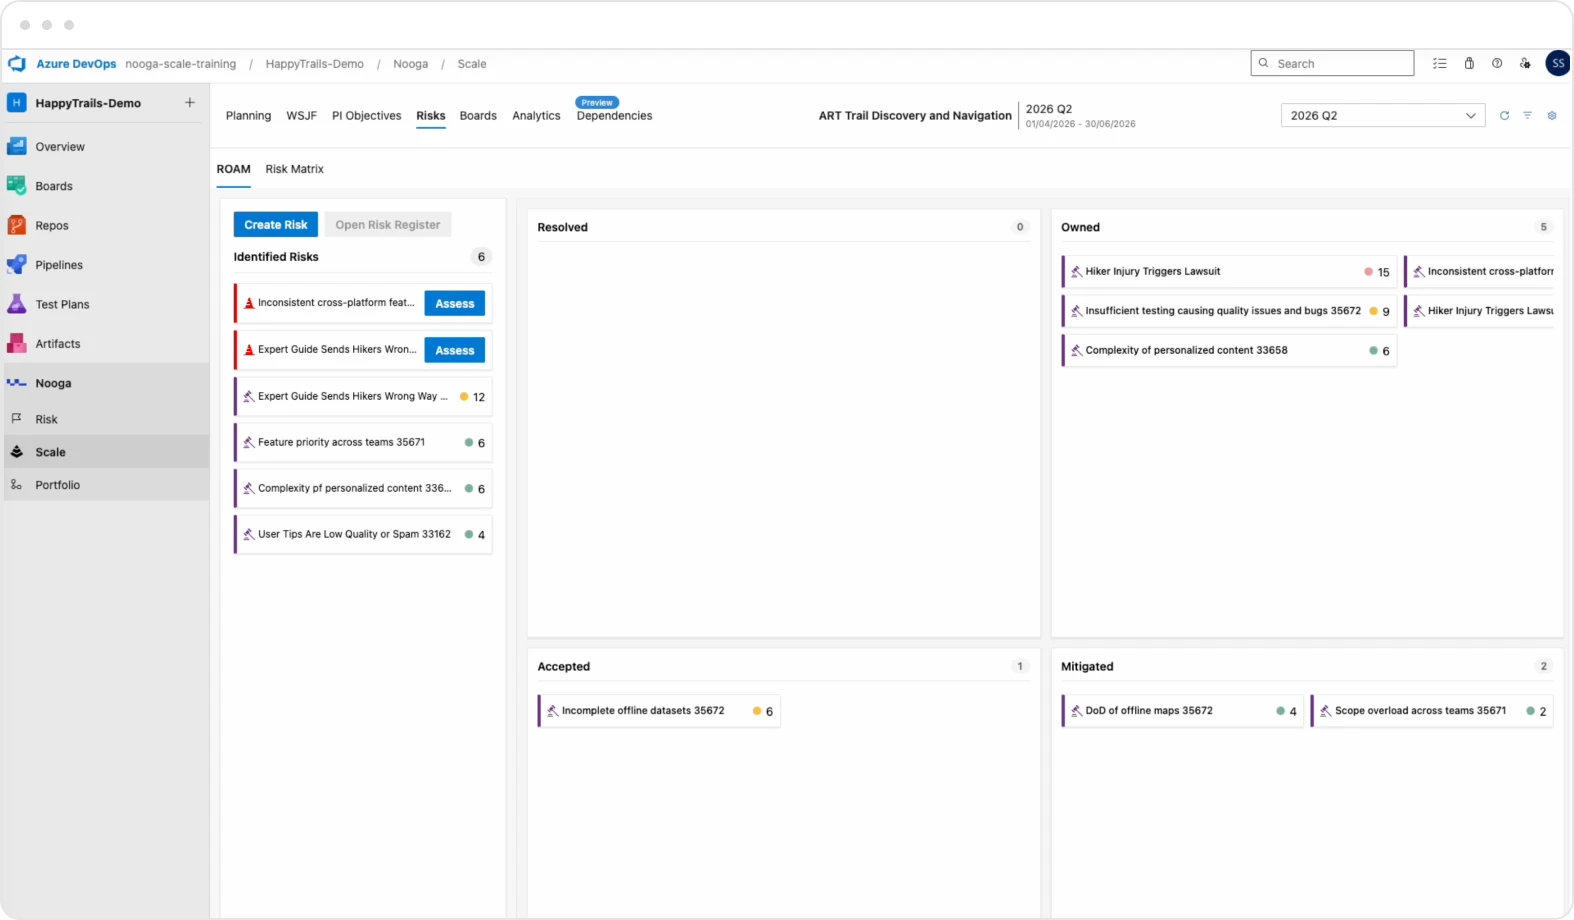
2. You're never starting from a blank page
Nooga's opt-in AI searches your risk register to suggest risks that are relevant to the work you're doing, so you're not starting from scratch every time. Risks aren't always easy to put into words: AI also helps surface root causes and likely effects, based on the context of the feature or epic itself. You decide what's relevant.
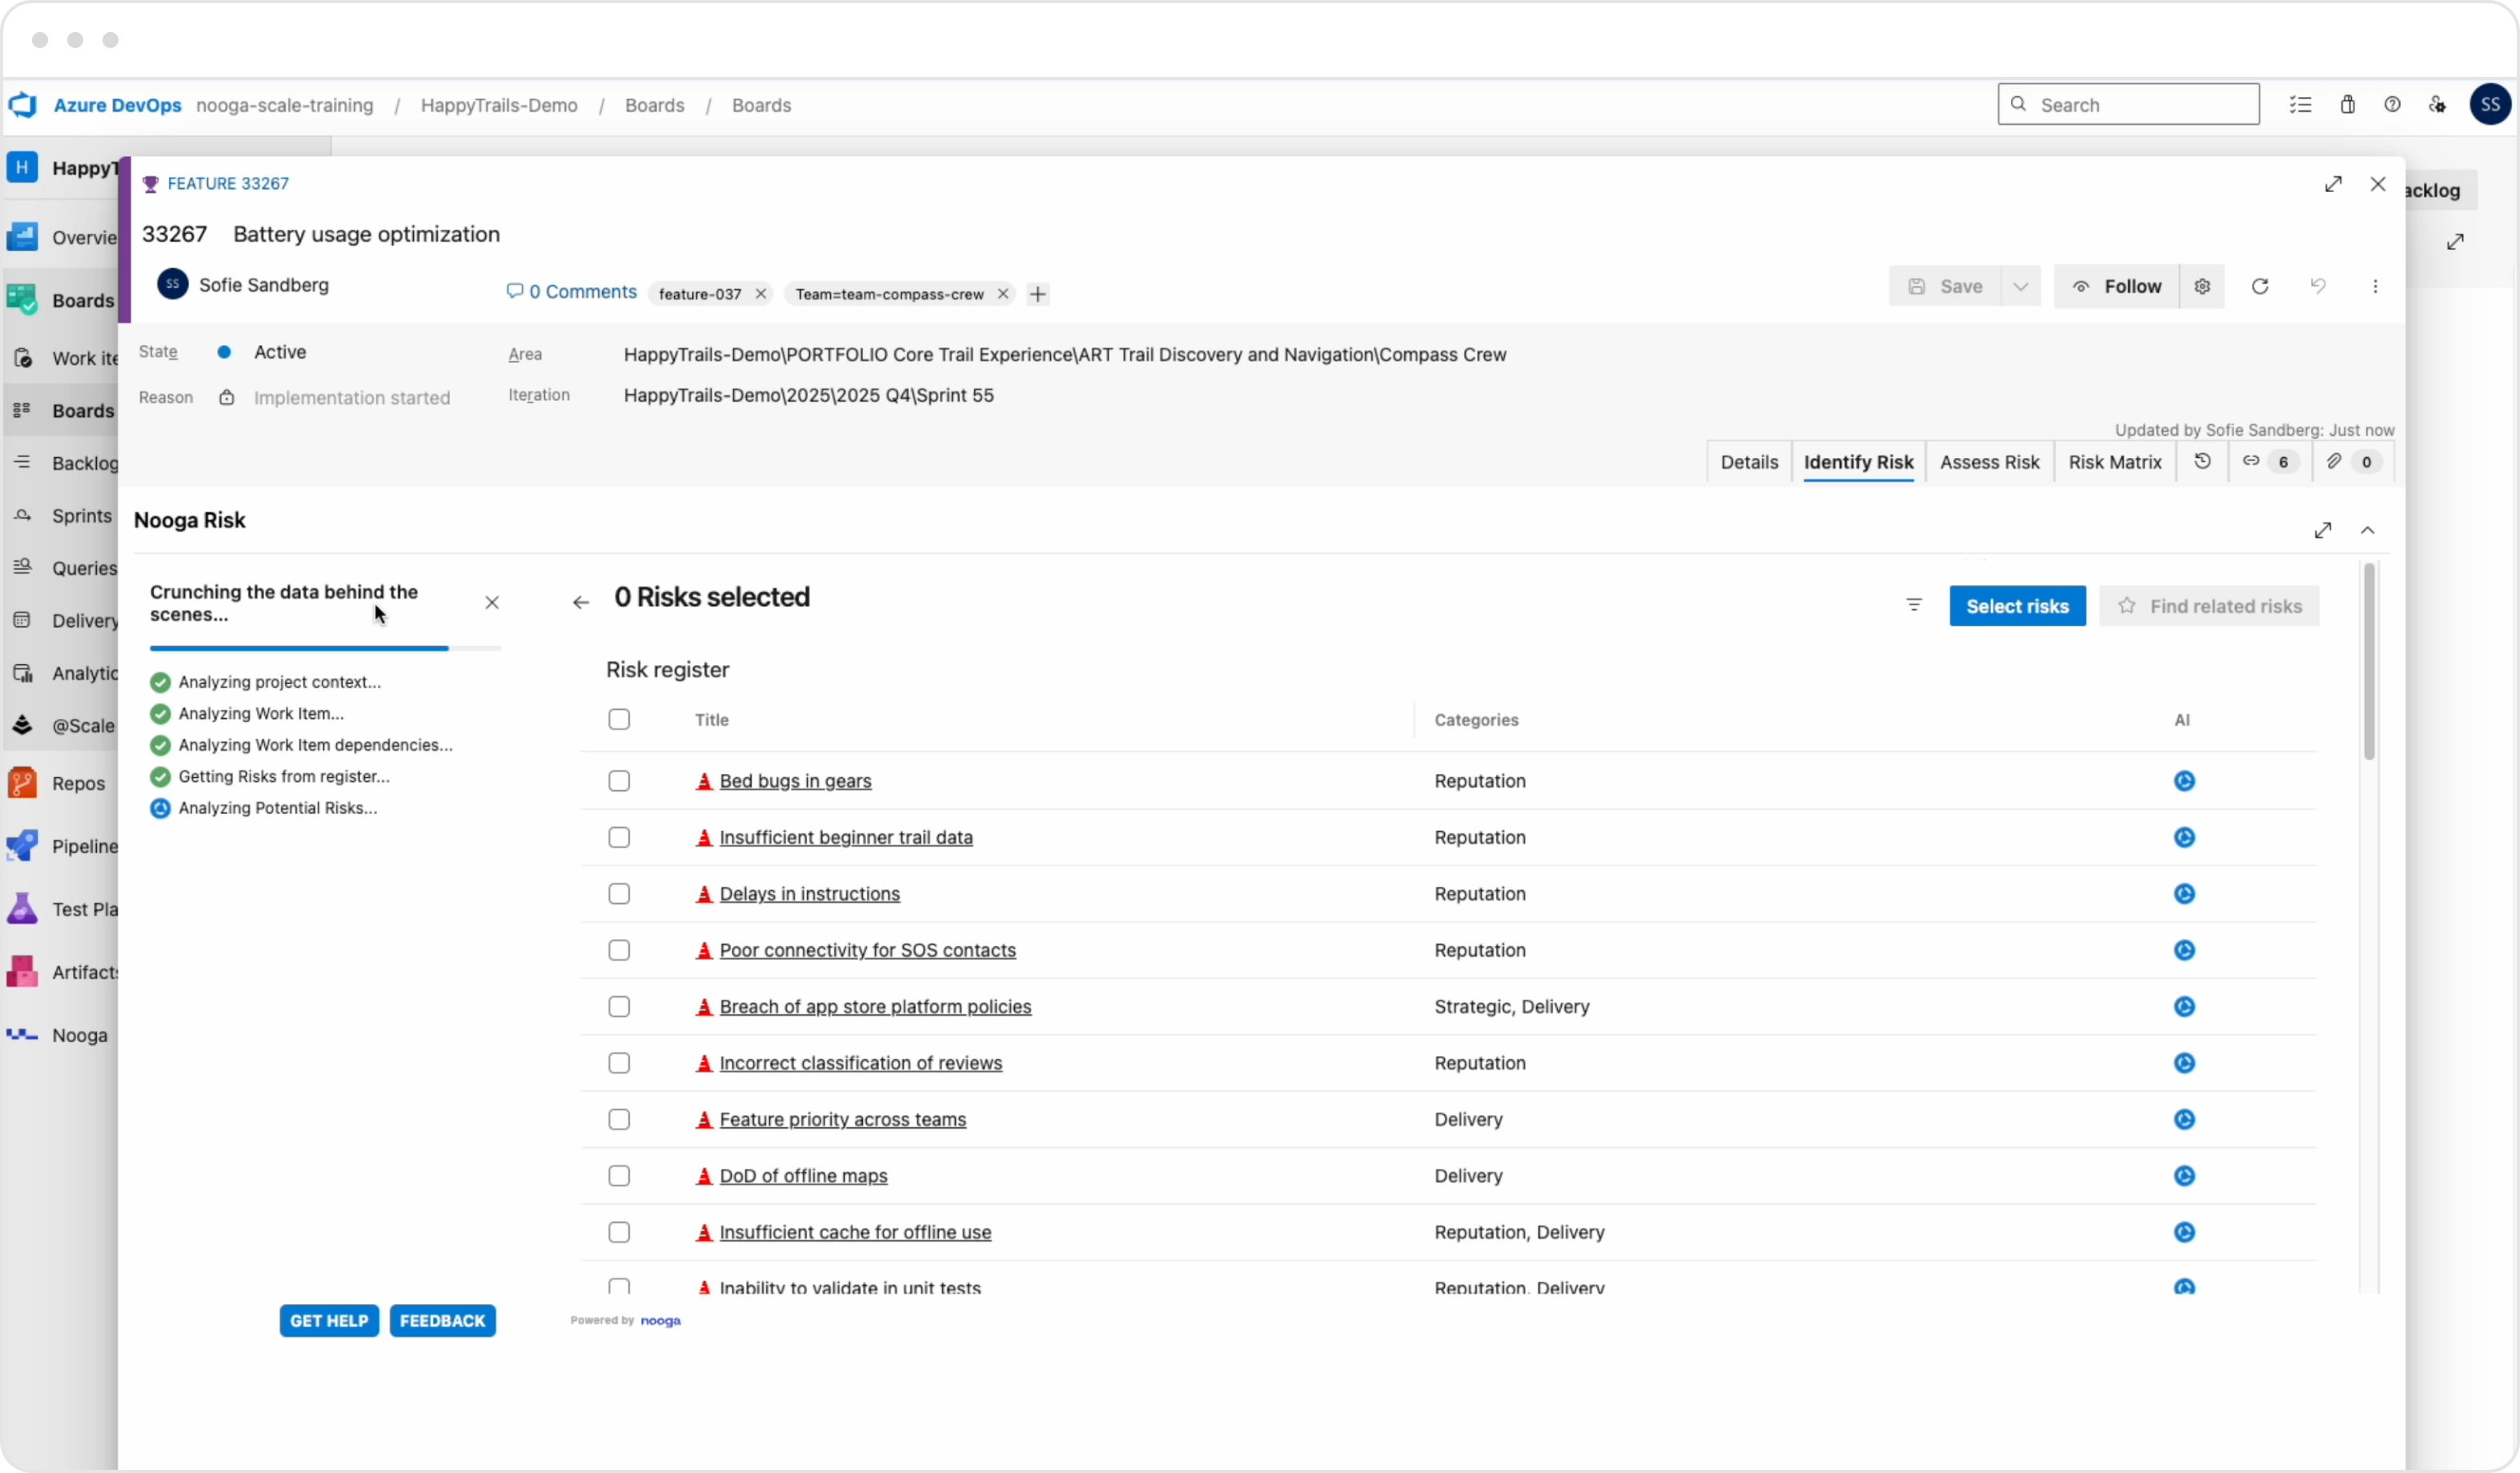
3. The right information for the right role, at the right time
Teams assess and prioritise the risks that matter most to the outcomes they've committed to. Developers raise and assess risks directly in their workflow, surfacing what's important at the moment a decision is being made. Executives, risk managers, and compliance teams get the register and matrix view, showing cross-organisational risk exposure at a glance.
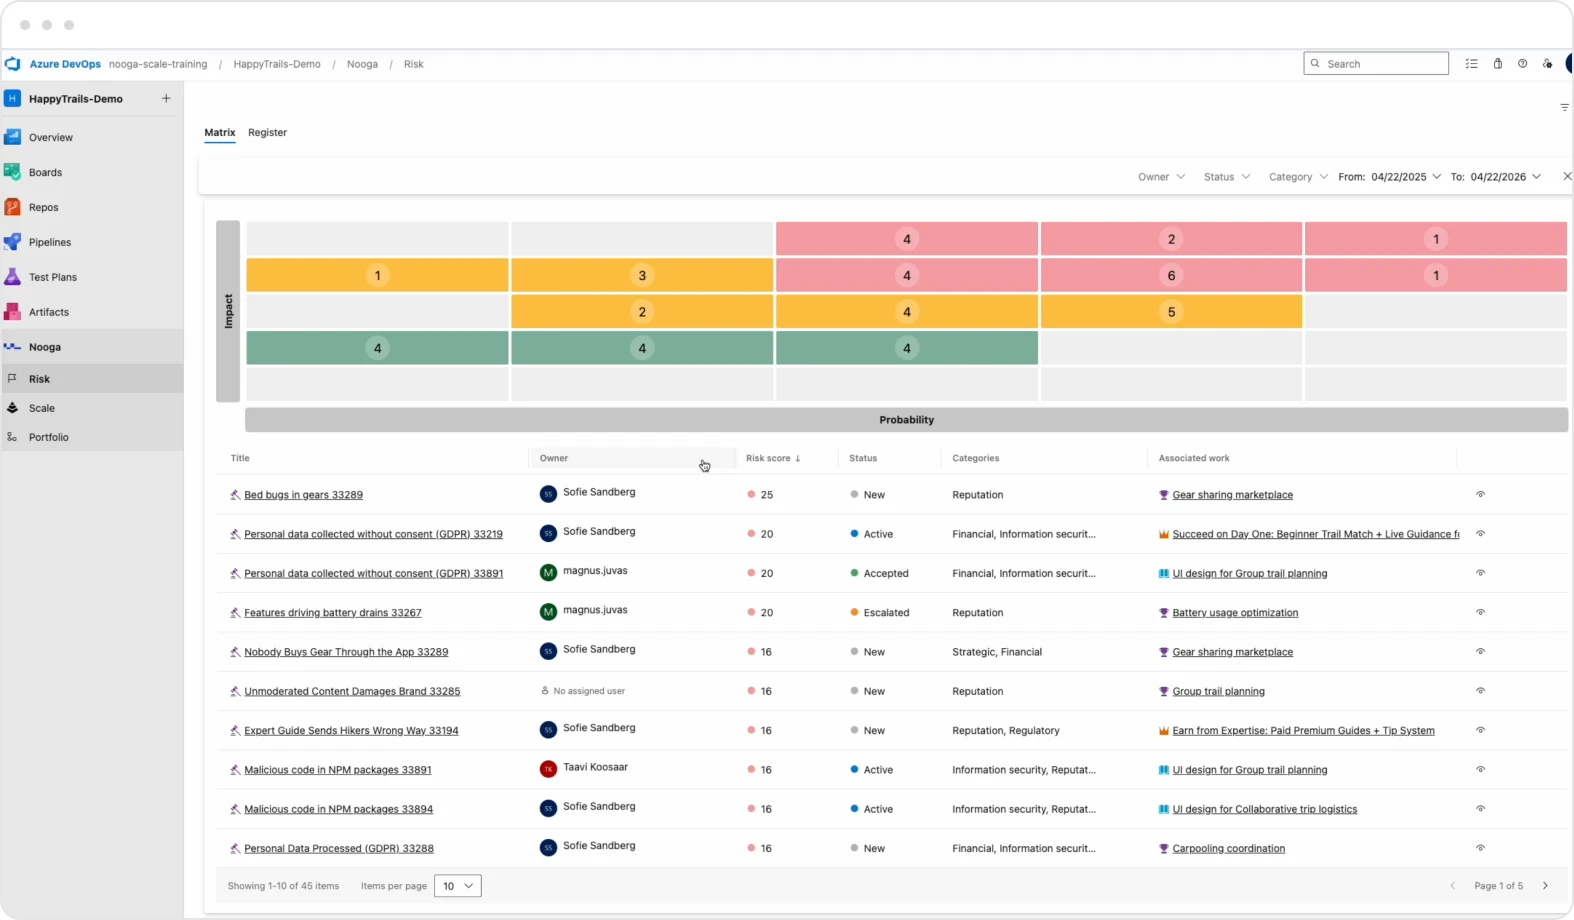
4. Audit evidence writes itself
Every risk decision is captured with a full audit trail — who approved what, when, and why. Risks above your tolerance threshold are automatically escalated to the right authorised approver, with the business justification recorded alongside the decision. Treatment activities go back into the backlog as work items, closing the loop between governance and delivery. All data stays in Azure DevOps.
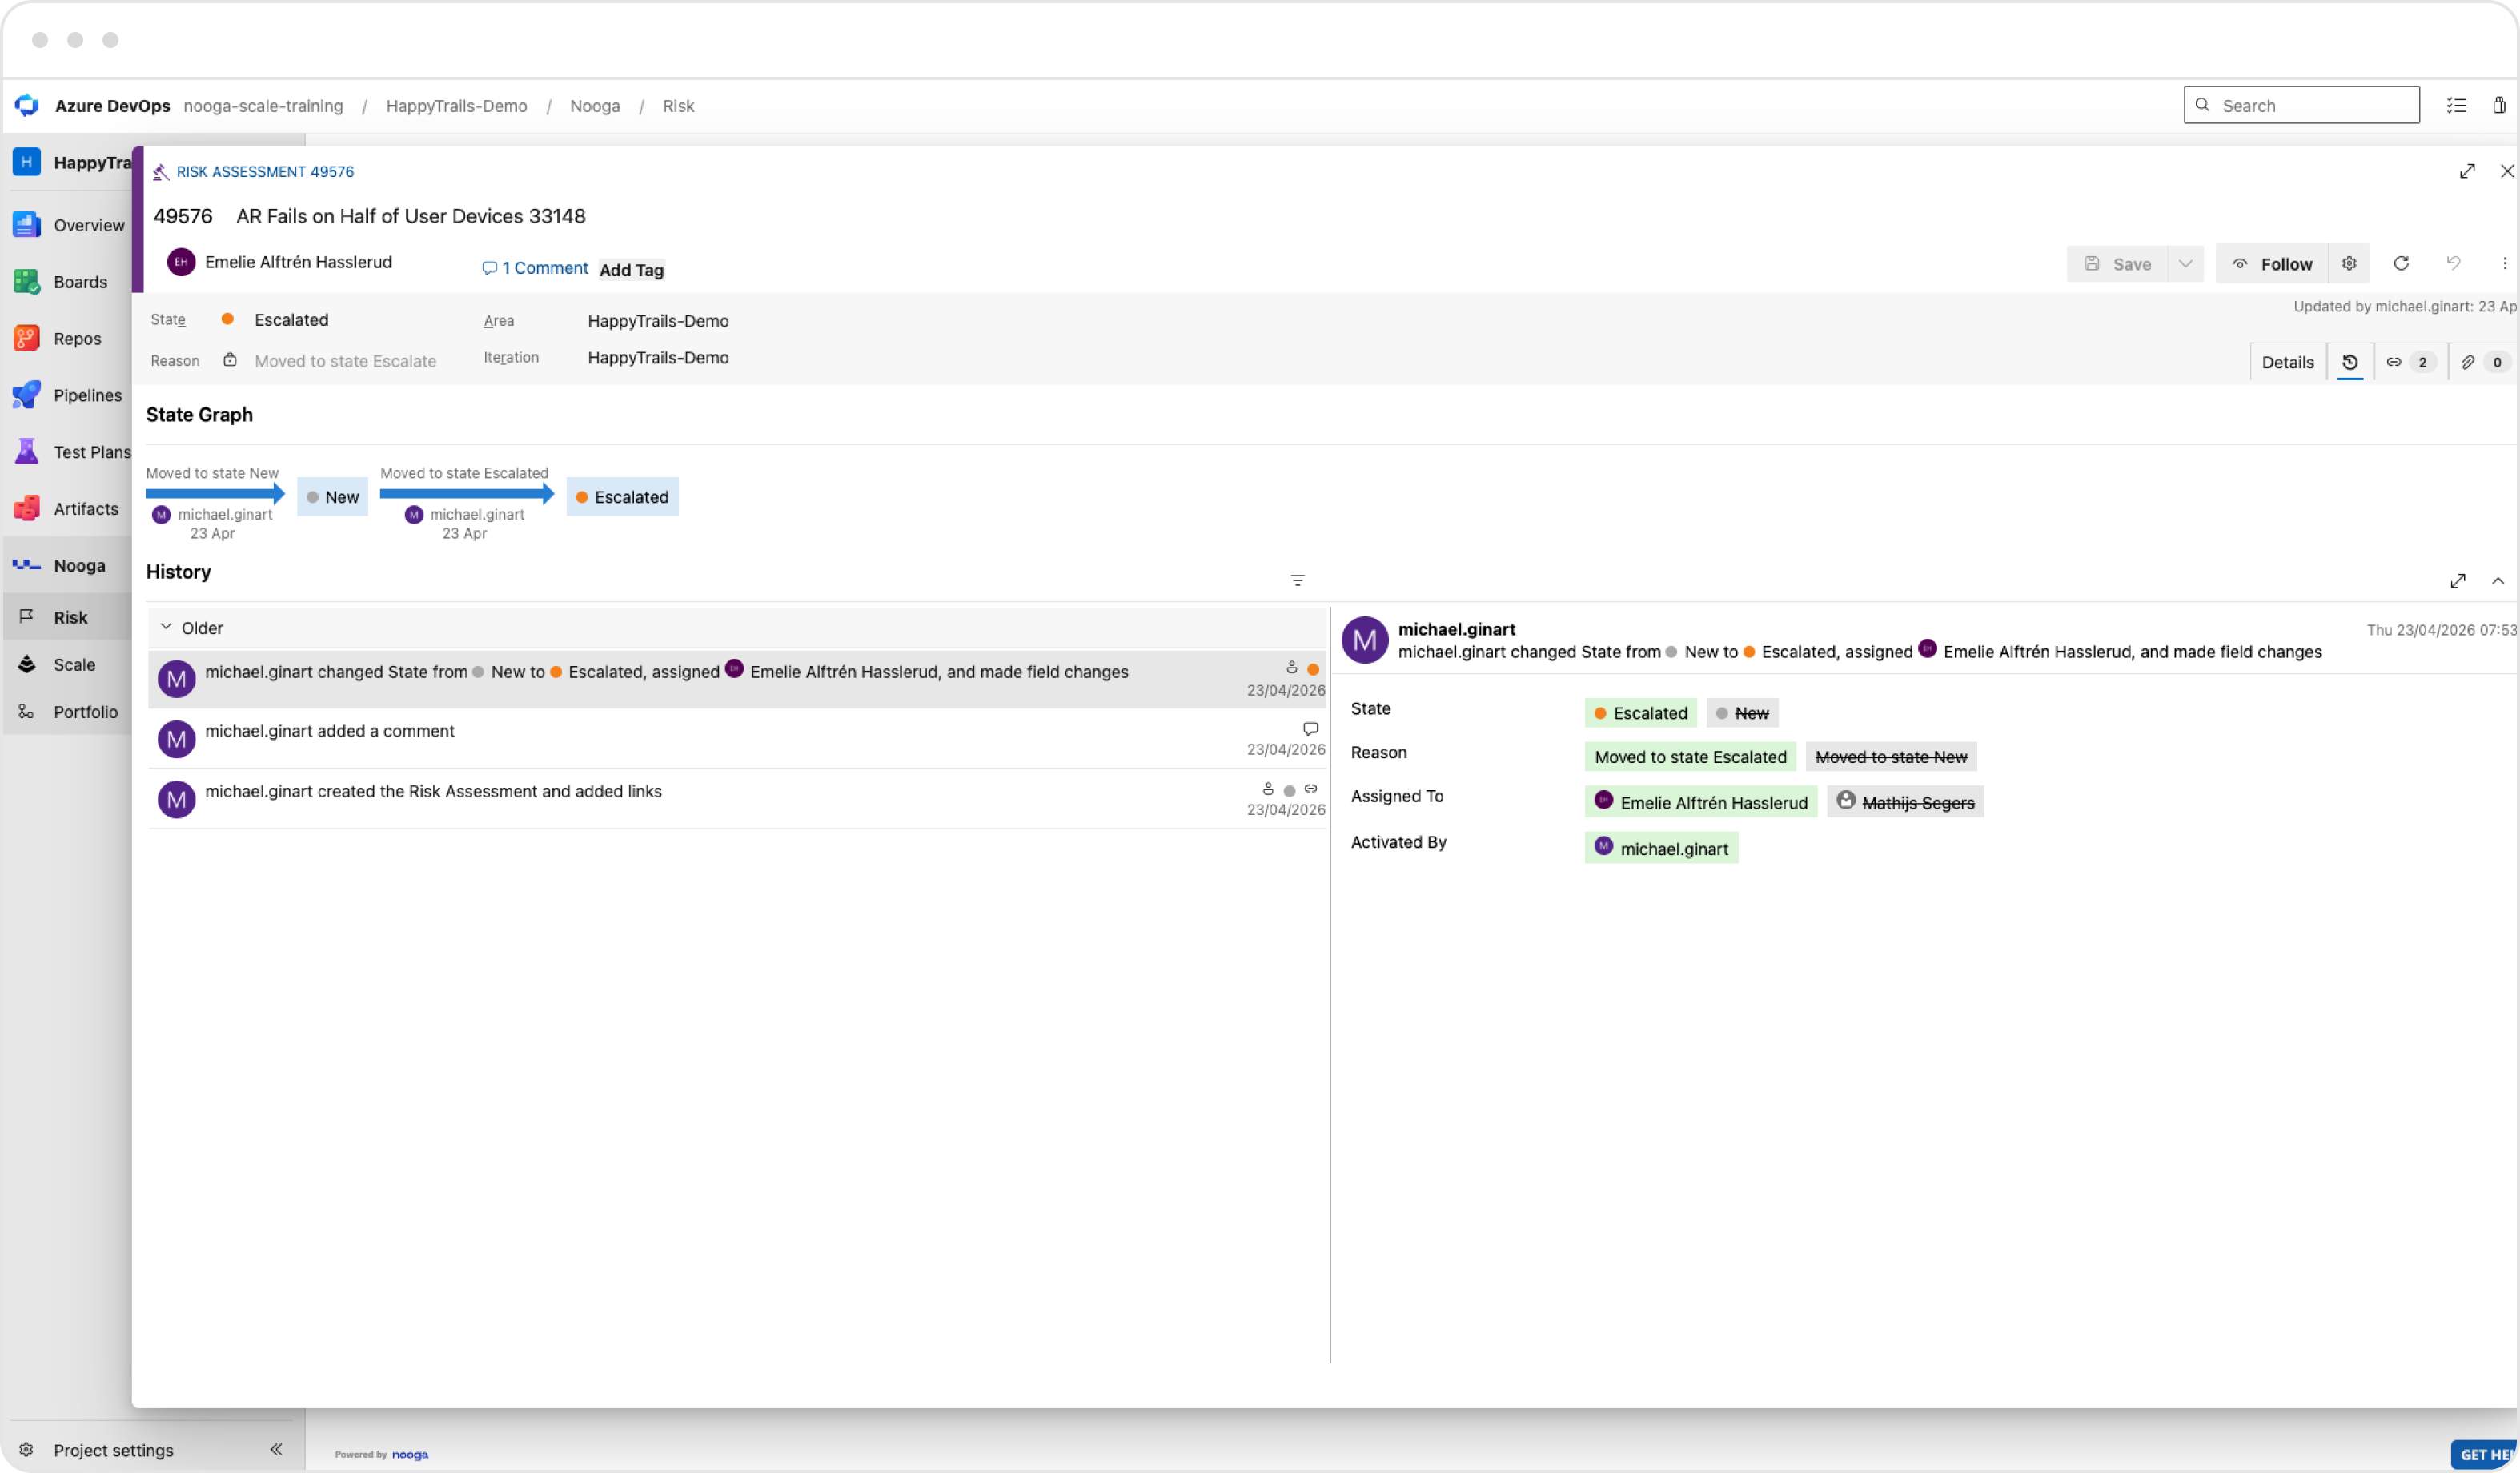
Azure DevOps Extensions
Risk Management as part of your delivery
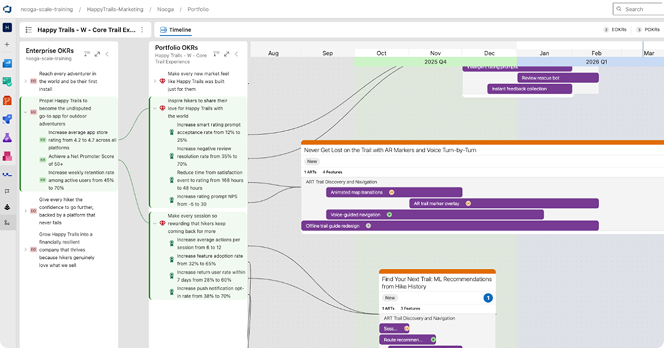
See the complete picture — from strategy to execution
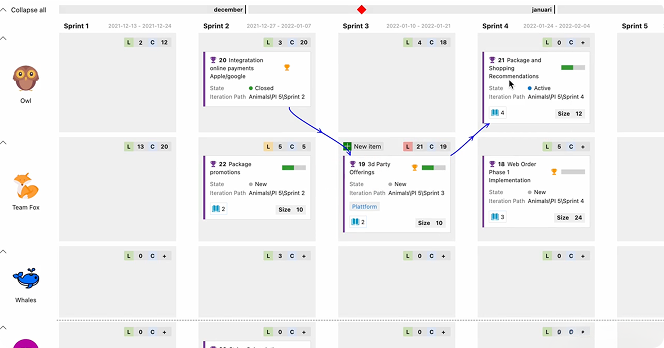
Agile planning at scale made easy
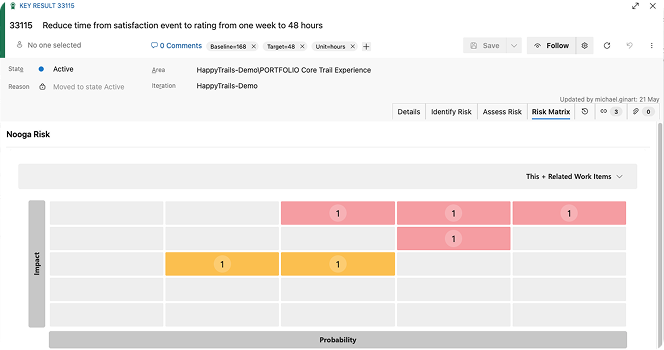
Risk management tool for the modern development world
FAQ
Will Nooga do the same for me?
Both. Developers see risks directly in their workflow - Nooga surfaces relevant risks on work items so teams can act in context, not fill out separate forms. Executives, risk managers, and compliance teams get comprehensive dashboards showing organisational risk exposure. One tool serves everyone: the people doing the work and the people responsible for governing it.
Nooga Risk supports regulations like DORA, NIS2, CRA, and to some extent ISO 27001 and GDPR, some requiring risks to be escalated for management or board approval, as well as risk management frameworks like COSO ERM and ISO 31000. Governance is configurable with customisable tolerance levels and automatic escalation.
Yes. Nooga Risk is a plugin that extends Azure DevOps. All you do in Nooga Risk stays in Azure DevOps, so you don't have to worry about integration, security, or data protection in a separate service.
They're separate Azure DevOps extensions and you can use either independently. Nooga Risk supports every step of the risk management process, from identifying and assessing risk through to treatment and follow-up. Together with Scale, risks get assessed and prioritised during planning and throughout the PI, with treatment activities living in the backlog so everyone stays in sync. Add Portfolio and those risks surface at a strategic level, tied to the enterprise and portfolio OKRs they affect.
Nooga
Get started with Nooga today
Embed governance into your Azure DevOps delivery workflows. No separate platform. All data stays in Azure DevOps.